
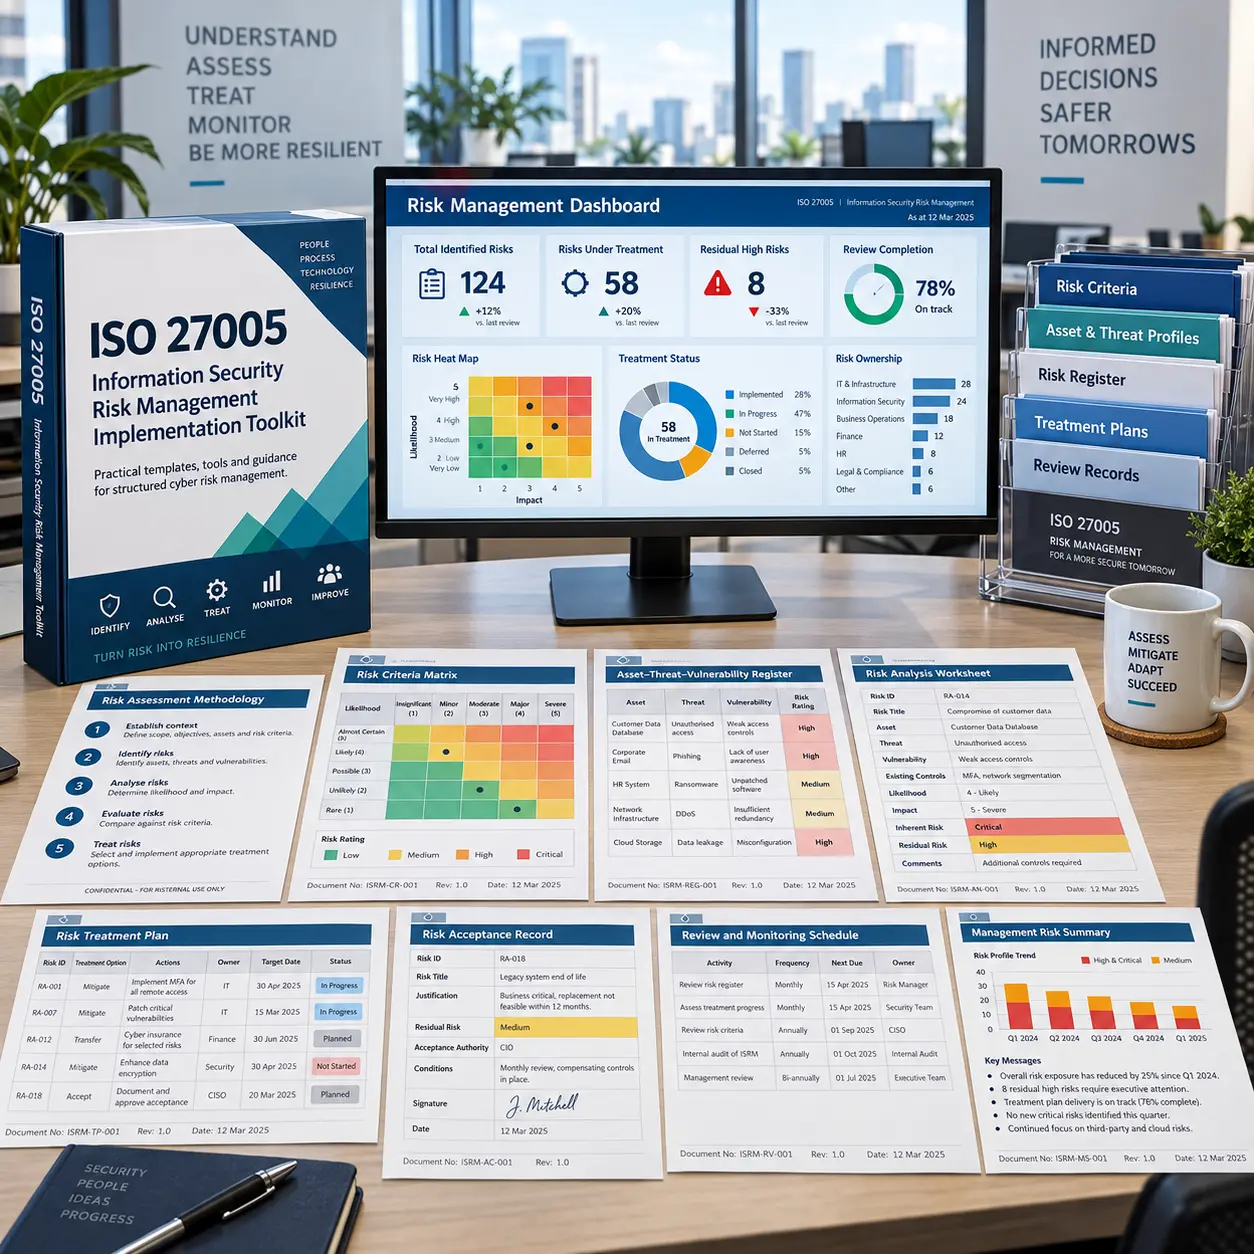
The ISO/IEC 27005:2022 Information Security Risk Management Toolkit provides a comprehensive, Easy To Use set of professional templates, practical guidance, registers, checklists, and dashboards to help organizations design, implement, monitor, and improve information security risk management effectively.
Aligned with ISO/IEC 27005:2022, this toolkit translates information security risk management guidance into actionable documentation for project initiation, risk context, risk criteria, risk assessment methodology, information asset inventory, risk identification, risk analysis, risk evaluation, treatment planning, third-party risk, communication, monitoring, review, maturity improvement, and operational handover.
Implementing information security risk management aligned with ISO/IEC 27005:2022 can be complex and time-consuming, especially for organizations that need consistent documentation, risk ownership, evidence records, dashboards, and practical procedures across multiple systems, departments, suppliers, and business locations.
The ISO/IEC 27005:2022 Information Security Risk Management Toolkit provides 106 professionally developed files across 12 structured folders in editable Word, Excel, and PowerPoint formats. It helps you quickly establish risk criteria, identify and assess risks, plan treatments, track residual risk, report KRIs, prepare governance evidence, and strengthen information security risk management.
Below is the structured list of documents included in the package. Use the quick navigation or expand each part to review the files before downloading the index file.
 Part 1. Project Initiation & Scope Setup
 Project Charter (ISO/IEC 27005 Implementation).docx Statement of Work (SOW) & Deliverables Matrix.docx Scope Statement (Organisation/System/Process).docx Project Communication Plan & Cadence.docx
 Project Plan & Milestone Tracker.xlsx Stakeholder Register & Engagement Plan.xlsx RACI Matrix (ISRM Roles).xlsx Assumptions, Constraints & Dependencies Log.xlsx Project RAID Log (Risks, Actions, Issues, Decisions).xlsx
Part 2. Risk Context & Risk Criteria Definition
Context Establishment Worksheet.xlsx Business Objectives & Risk Drivers Mapping.xlsx Risk Criteria Definition Template.xlsx Impact Rating Scale (Multi-Domain) Template.xlsx Likelihood Rating Scale Template.xlsx Risk Matrix / Heatmap Configuration Sheet.xlsx Risk Appetite & Risk Tolerance Statement.docx Risk Acceptance Criteria & Approval Thresholds.docx Risk Taxonomy & Classification Standard.docx
Part 3. Risk Assessment Methodology & Standards
Risk Assessment Methodology (Qual/Quant/Hybrid).docx Risk Scenario Definition Guide & Templates.docx Risk Workshop Facilitation Pack (Agenda, Scripts, Outputs).docx Risk ID Naming Convention & Version Control Rulebook.docx Evidence Requirements & Quality Checklist.docx Asset-Threat-Vulnerability Mapping Template.xlsx Control Baseline Mapping Sheet (ISO/IEC 27001 Annex A).xlsx Data Classification & Asset Criticality Scoring.xlsx Risk Scoring Model Configuration Workbook.xlsx
Part 4. Information Asset Inventory & Ownership
Information Asset Register (Enterprise).xlsx Asset Ownership & Custodian Register.xlsx Business Process-Asset Mapping Sheet.xlsx System Inventory (Applications/Servers/Cloud Services).xlsx Data Inventory & Data Classification Register.xlsx Interface & Integration Inventory.xlsx Third-Party Asset Touchpoints Register.xlsx Data Flow Diagram Template.pptx System Boundary / Context Diagram Template.pptx
Part 5. Risk Identification
Risk Identification Checklist Pack.docx Incident-to-Risk Conversion Form.docx Risk Statement Standard (How-to Write Risks).docx Risk Identification Workshop Capture Sheet.xlsx Threat Library & Threat Taxonomy Workbook.xlsx Vulnerability & Findings Register.xlsx Risk Scenario Catalog (Master List).xlsx Control Gaps & Weaknesses Log.xlsx Emerging Risk Intake & Triage Form.xlsx
Part 6. Risk Analysis & Risk Scoring
Inherent Risk Scoring Worksheet.xlsx Current Controls Assessment Worksheet.xlsx Control Effectiveness Scoring Model.xlsx Residual Risk Calculation Sheet.xlsx Risk Drivers & Evidence Log.xlsx Assumptions & Uncertainty Log.xlsx Risk Interdependency / Concentration Analysis.xlsx Key Risk Indicator (KRI) Definition & Thresholds.xlsx One-Page Risk Profile (Executive Template).docx
Part 7. Risk Evaluation, Prioritisation & Decisions
Risk Prioritisation Matrix Template.xlsx Risk Evaluation Summary (By BU/System).xlsx Risk Committee Decision Log.xlsx Risk Treatment Decision Form.docx Risk Acceptance Request & Approval Form.docx Control Exception / Deviation Request Form.docx Risk Escalation Criteria & Workflow.docx Risk Aggregation Executive Report Slides.pptx Top Risks Dashboard (Board Pack).pptx
Part 8. Risk Treatment Planning & Control Governance
Risk Treatment Plan (RTP) Master Workbook.xlsx Risk Treatment Action Tracker.xlsx Control Implementation Plan & Schedule.xlsx Control Owner Accountability & Attestation.xlsx Budget, Cost & Benefits Justification.xlsx Residual Risk Forecast & Target Risk Levels.xlsx Compensating Controls Justification Form.docx Security / Control Requirements Specification.docx Verification & Validation Plan for Treatments.docx
Part 9. Third-Party & Supply Chain Risk Management
Third-Party Risk Assessment (TPRA) Questionnaire Pack.docx Contract Security Clauses Checklist.docx SLA/OLA Security Addendum Template.docx Supplier Risk Scoring & Due Diligence Workbook.xlsx Third-Party Inventory & Criticality Register.xlsx Third-Party Control Evidence Tracking Log.xlsx Vendor Remediation / Corrective Action Tracker.xlsx Sub-processor / Fourth-Party Register.xlsx Concentration Risk & Critical Supplier Register.xlsx
Part 10. Risk Communication, Consultation & Reporting
Risk Communication & Consultation Plan.docx Risk Governance Charter & Committee TOR.docx Risk Review Meeting Agenda & Minutes Template.docx Risk Register Publication & Access Control Rules.docx Risk Escalation & Notification Procedure.docx Reporting Calendar & Distribution List.xlsx Monthly Risk Reporting Deck (Operations).pptx Quarterly Risk Reporting Deck (Management/Board).pptx Risk Awareness & Training Materials Slides.pptx
Part 11. Monitoring, Review & Continuous Operation
Enterprise Risk Register (Master).xlsx KRI Monitoring Dashboard & Alerts.xlsx Control Testing Plan & Schedule.xlsx Control Testing / Effectiveness Review Workbook.xlsx Risk Reassessment Triggers & Change Log.xlsx Risk Action / Remediation Tracking Log.xlsx Internal Audit Evidence Pack Index.xlsx Risk Closure & Lessons Learned Form.docx Management Review Pack (Risk Performance).pptx
Part 12. Continuous Improvement, Maturity & Handover
ISRM Process Maturity Assessment Workbook.xlsx Continuous Improvement Backlog & Prioritisation.xlsx Roles Competency Matrix & Training Plan.xlsx Post-Implementation Review (PIR) Template.docx 30-60-90 Day Stabilisation & Benefits Review.docx Handover Checklist (Documents, Access, Cadence).docx Operating Model & SOP Playbook (ISRM).docx GRC/IRM Tool Configuration Guide.docxReview the complete file index, preview free sample templates, or check the purchase and payment guide.
| Date File Updated | 25/03/2025 |
| File Format | pdf, xls, doc, docx, xlsx, pptx |
| No. of files | 106 Files, 12 Folders |
| File download size | 2.95 MB (.rar) |
| Language |  English |
| Purchase code | ISO27005-Toolkits |
The ISO Toolkit has helped us structure our implementation work clearly. It gave our team practical templates, organized procedures, and a reliable starting point for building our management system documentation.
After using the ISO Toolkit, our ISO preparation became much more organized. The documents are professional, easy to adapt, and helpful for aligning internal teams around clear compliance requirements.
Our consultants and internal managers found the toolkit very practical. It saved time, improved documentation consistency, and gave us a better framework for ISO implementation across departments.
The toolkit provides a strong foundation for ISO best practices. It helped us organize policies, procedures, records, and improvement actions in a way that is simple to maintain.
The ISO Toolkit brought structure to our compliance documentation and reduced the workload for our implementation team. It allowed us to focus more on improving processes instead of starting documents from scratch.
The ISO Toolkit is practical, well arranged, and easy to customize. It helped replace scattered files with a more complete document set for managing our ISO implementation activities.
The toolkit is very straightforward to use. It gave our team a clear implementation path, helped define responsibilities, and made ISO documentation easier for non-specialists to understand.
The ISO Toolkit gave us a better understanding of management system requirements and provided a user-friendly way to improve processes, controls, and internal documentation.
The toolkit helped me organize our ISO training, document review, and implementation planning. It made the entire preparation process more focused and easier to communicate with the team.
Excellent ISO Toolkit. It is highly useful for managers, consultants, and implementation teams who need practical documents to support ISO certification readiness.
A very useful toolkit and one of the most practical document sets I have used. It provides clear templates that can be adapted quickly for different ISO implementation needs.
These ISO Toolkits increased my confidence in managing implementation work. They helped us prepare documentation, assign responsibilities, and move toward a more mature management system.