
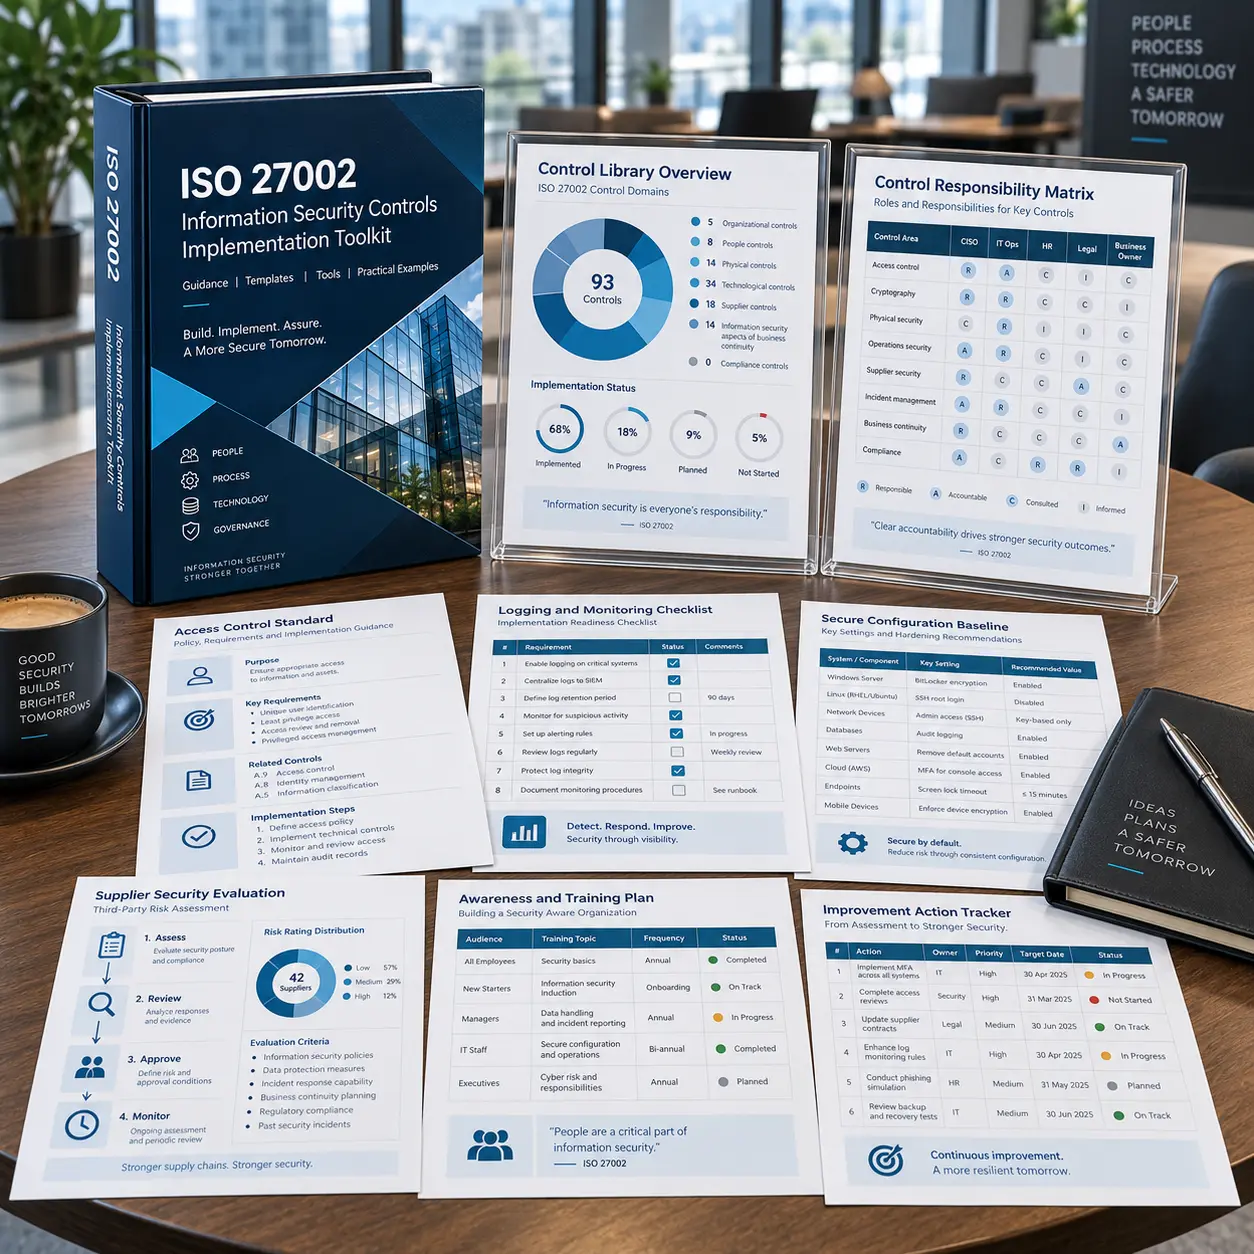
The ISO/IEC 27002:2022 Information Security Controls Implementation Toolkit provides a comprehensive, Easy To Use set of professional templates, practical guidance, registers, checklists, and dashboards to help organizations design, implement, monitor, and improve information security controls effectively.
Aligned with ISO/IEC 27002:2022, this toolkit translates information security control guidance into actionable documentation for governance, asset management, risk treatment, control selection, access control, cryptography, physical security, operations security, network security, application security, supplier security, incident management, business continuity, compliance, audit, awareness, reporting, continual improvement, and record management.
Implementing controls aligned with ISO/IEC 27002:2022 can be complex and time-consuming, especially for organizations that need consistent documentation, control ownership, evidence records, dashboards, and practical procedures across multiple systems, departments, suppliers, and business locations.
The ISO/IEC 27002:2022 Information Security Controls Implementation Toolkit provides 232 professionally developed files across 18 structured folders in editable Word, Excel, and PowerPoint formats. It helps you quickly implement controls, standardize documentation, track security performance, prepare audit evidence, and strengthen information security governance.
Below is the structured list of documents included in the package. Use the quick navigation or expand each part to review the files before downloading the index file.
 Part 1. Program Initiation & Governance Setup
 ISMS Program Charter.docx Information Security Governance Framework.docx ISMS Scope Definition.docx ISMS Policy Framework Structure.docx Information Security Policy (Master).docx Information Security Objectives Definition.docx ISMS Communication Plan.docx Information Security Roles & Responsibilities.docx Regulatory & Compliance Framework Mapping.docx ISMS Implementation Roadmap.docx
 Stakeholder Register.xlsx ISMS RACI Matrix.xlsx Information Security Objectives & KPI Register.xlsx Regulatory & Compliance Requirements Register.xlsx Governance Meeting Schedule.xlsx ISMS Budget Tracker.xlsx
 ISMS Program Kickoff Slides.pptx Executive Awareness Slides.pptx
Part 2. Asset Management & Classification
Asset Management Policy.docx Asset Classification Policy.docx Data Classification & Labeling Guidelines.docx Asset Handling Procedures.docx Acceptable Use Policy.docx Information Handling Standard.docx Media Handling & Disposal Procedure.docx Asset Inventory Register.xlsx Information Asset Ownership Register.xlsx Data Classification Register.xlsx Media Handling & Disposal Log.xlsx Asset Transfer Register.xlsx Critical Asset Register.xlsx Asset Classification Awareness Slides.pptx
Part 3. Risk Management & Treatment
Risk Management Policy.docx Risk Management Methodology.docx Risk Assessment Procedure.docx Risk Treatment Strategy.docx Risk Acceptance Criteria.docx Risk Evaluation Criteria.docx Business Impact Analysis Methodology.docx Risk Assessment Register.xlsx Risk Treatment Plan.xlsx Risk Scenario Library.xlsx Threat & Vulnerability Register.xlsx Business Impact Analysis (BIA).xlsx Risk Heat Map.xlsx Risk Acceptance Log.xlsx Risk Assessment Workshop Slides.pptx Risk Reporting Slides.pptx
Part 4. Control Selection & Implementation
Control Implementation Strategy.docx Control Design Specification.docx Control Implementation Guidelines.docx Compensating Control Justification.docx Control Gap Assessment Report.docx Control Standard Operating Procedures.docx Statement of Applicability (SoA).xlsx Control Implementation Plan.xlsx Control Mapping Matrix.xlsx Control Implementation Tracker.xlsx Control Ownership Register.xlsx Control Effectiveness Tracking.xlsx Control Implementation Overview Slides.pptx Control Gap Assessment Presentation.pptx
Part 5. Access Control & Identity Management
Access Control Policy.docx Identity & Access Management Standard.docx User Access Management Procedure.docx Privileged Access Management Procedure.docx Password Policy.docx Authentication Standard.docx Identity Lifecycle Management Procedure.docx User Access Request Form.xlsx Privileged Access Register.xlsx Access Review Log.xlsx Segregation of Duties Matrix.xlsx Dormant Account Register.xlsx Access Violation Log.xlsx IAM Awareness Slides.pptx
Part 6. Cryptography & Data Protection
Cryptographic Policy.docx Encryption Standard.docx Encryption Key Management Procedure.docx Data Protection Policy.docx Data Retention & Disposal Policy.docx Data Masking & Anonymization Guidelines.docx Backup & Restore Procedure.docx Secure Data Transfer Standard.docx Key Inventory Register.xlsx Backup Log Register.xlsx Data Retention Schedule.xlsx Encryption Usage Register.xlsx Data Protection Awareness Slides.pptx
Part 7. Physical & Environmental Security
Physical Security Policy.docx Facility Access Control Procedure.docx Secure Area Definition.docx Equipment Security Standard.docx Clean Desk & Clear Screen Policy.docx Environmental Security Procedure.docx Visitor Log Register.xlsx Physical Access Register.xlsx Equipment Security Checklist.xlsx Environmental Controls Checklist.xlsx Physical Security Incident Log.xlsx Physical Security Awareness Slides.pptx
Part 8. Operations Security
Operations Security Policy.docx Change Management Procedure.docx Configuration Management Standard.docx Patch Management Procedure.docx System Monitoring Procedure.docx Log Management Policy.docx Backup Management Procedure.docx Job Scheduling Procedure.docx Change Request Log.xlsx Configuration Management Register.xlsx Patch Management Log.xlsx Backup Monitoring Report.xlsx System Monitoring Log.xlsx Job Execution Log.xlsx Operations Security Awareness Slides.pptx
Part 9. Network & Infrastructure Security
Network Security Policy.docx Network Architecture Standard.docx Secure Configuration Baseline.docx Firewall Management Procedure.docx Vulnerability Management Procedure.docx Network Segmentation Standard.docx Firewall Rule Register.xlsx Vulnerability Scan Report.xlsx Network Access Control Register.xlsx Network Device Inventory.xlsx Patch Compliance Dashboard.xlsx Network Security Overview Slides.pptx
Part 10. Secure Development & Application Security
Secure Development Policy.docx Secure Coding Standards.docx Application Security Standard.docx DevSecOps Guidelines.docx Software Development Lifecycle Policy.docx Code Review Procedure.docx Application Security Requirements Checklist.xlsx Code Review Checklist.xlsx DevSecOps Pipeline Checklist.xlsx Software Inventory Register.xlsx Open Source Risk Assessment.xlsx Application Vulnerability Log.xlsx Secure Development Awareness Slides.pptx
Part 11. Supplier & Third-Party Security
Supplier Security Policy.docx Third-Party Risk Management Procedure.docx Vendor Security Requirements Standard.docx Third-Party Security Agreement Template.docx Outsourcing Security Policy.docx Third-Party Risk Assessment.xlsx Supplier Register.xlsx Vendor Due Diligence Checklist.xlsx Outsourcing Security Checklist.xlsx Supplier Performance Review.xlsx Third-Party Incident Log.xlsx Third-Party Risk Awareness Slides.pptx
Part 12. Incident Management
Information Security Incident Management Policy.docx Incident Response Plan.docx Incident Response Procedure.docx Incident Classification Standard.docx Root Cause Analysis Template.docx Incident Response Playbooks.docx Digital Forensics Guidelines.docx Incident Classification Matrix.xlsx Incident Log Register.xlsx Lessons Learned Register.xlsx Incident Response KPI Dashboard.xlsx Incident Response Training Slides.pptx
Part 13. Business Continuity & Disaster Recovery
Business Continuity Policy.docx Business Continuity Strategy.docx Business Continuity Plan (BCP).docx Disaster Recovery Plan (DRP).docx Crisis Communication Plan.docx DR Testing Procedure.docx Business Impact Analysis (Detailed).xlsx DR Test Plan.xlsx DR Test Report.xlsx Recovery Time Objective (RTO/RPO) Register.xlsx Critical Service Register.xlsx BCP/DR Awareness Slides.pptx
Part 14. Compliance, Audit & Assurance
Internal Audit Policy.docx Audit Procedure.docx Audit Report Template.docx Compliance Monitoring Procedure.docx Corrective Action Procedure.docx Internal Audit Plan.xlsx Audit Checklist.xlsx Nonconformity Register.xlsx Corrective Action Plan.xlsx Compliance Monitoring Report.xlsx Control Effectiveness Assessment.xlsx Evidence Collection Register.xlsx Audit Results Presentation Slides.pptx
Part 15. Security Awareness & Training
Security Awareness Policy.docx Security Awareness Program Plan.docx Training Procedure.docx Employee Acknowledgement Form.docx Phishing Simulation Plan.xlsx Training Attendance Register.xlsx Awareness Campaign Calendar.xlsx Security Quiz & Assessment.xlsx Training Effectiveness Evaluation.xlsx Security Awareness Training Slides.pptx Phishing Awareness Slides.pptx
Part 16. Monitoring, Metrics & Reporting
Security Monitoring Strategy.docx Reporting Procedure.docx Management Review Procedure.docx Security Metrics Dashboard.xlsx KPI/KRI Register.xlsx Security Performance Scorecard.xlsx Risk Trend Analysis.xlsx Control Maturity Assessment.xlsx SLA Monitoring Dashboard.xlsx Monthly Security Report Slides.pptx Management Review Slides.pptx
Part 17. Continuous Improvement & ISMS Maintenance
Continuous Improvement Policy.docx ISMS Review Procedure.docx Change Management for ISMS.docx Continuous Improvement Register.xlsx Improvement Action Tracker.xlsx Policy Review Schedule.xlsx Document Version Control Register.xlsx Change Impact Assessment.xlsx ISMS Maturity Model Assessment.xlsx ISMS Improvement Roadmap Slides.pptx
Part 18. Documentation & Record Management
Document Control Procedure.docx Record Management Policy.docx Document Classification Standard.docx Document Register.xlsx Record Retention Schedule.xlsx Document Approval Log.xlsx Document Change Log.xlsx Confidential Document Register.xlsx Archive Index.xlsx Document Control Awareness Slides.pptxReview the complete file index, preview free sample templates, or check the purchase and payment guide.
| Date File Updated | 25/03/2025 |
| File Format | pdf, xls, doc, docx, xlsx, pptx |
| No. of files | 232 Files, 18 Folders |
| File download size | 7.50 MB (.rar) |
| Language |  English |
| Purchase code | ISO27002-Toolkits |
The ISO Toolkit has helped us structure our implementation work clearly. It gave our team practical templates, organized procedures, and a reliable starting point for building our management system documentation.
After using the ISO Toolkit, our ISO preparation became much more organized. The documents are professional, easy to adapt, and helpful for aligning internal teams around clear compliance requirements.
Our consultants and internal managers found the toolkit very practical. It saved time, improved documentation consistency, and gave us a better framework for ISO implementation across departments.
The toolkit provides a strong foundation for ISO best practices. It helped us organize policies, procedures, records, and improvement actions in a way that is simple to maintain.
The ISO Toolkit brought structure to our compliance documentation and reduced the workload for our implementation team. It allowed us to focus more on improving processes instead of starting documents from scratch.
The ISO Toolkit is practical, well arranged, and easy to customize. It helped replace scattered files with a more complete document set for managing our ISO implementation activities.
The toolkit is very straightforward to use. It gave our team a clear implementation path, helped define responsibilities, and made ISO documentation easier for non-specialists to understand.
The ISO Toolkit gave us a better understanding of management system requirements and provided a user-friendly way to improve processes, controls, and internal documentation.
The toolkit helped me organize our ISO training, document review, and implementation planning. It made the entire preparation process more focused and easier to communicate with the team.
Excellent ISO Toolkit. It is highly useful for managers, consultants, and implementation teams who need practical documents to support ISO certification readiness.
A very useful toolkit and one of the most practical document sets I have used. It provides clear templates that can be adapted quickly for different ISO implementation needs.
These ISO Toolkits increased my confidence in managing implementation work. They helped us prepare documentation, assign responsibilities, and move toward a more mature management system.