
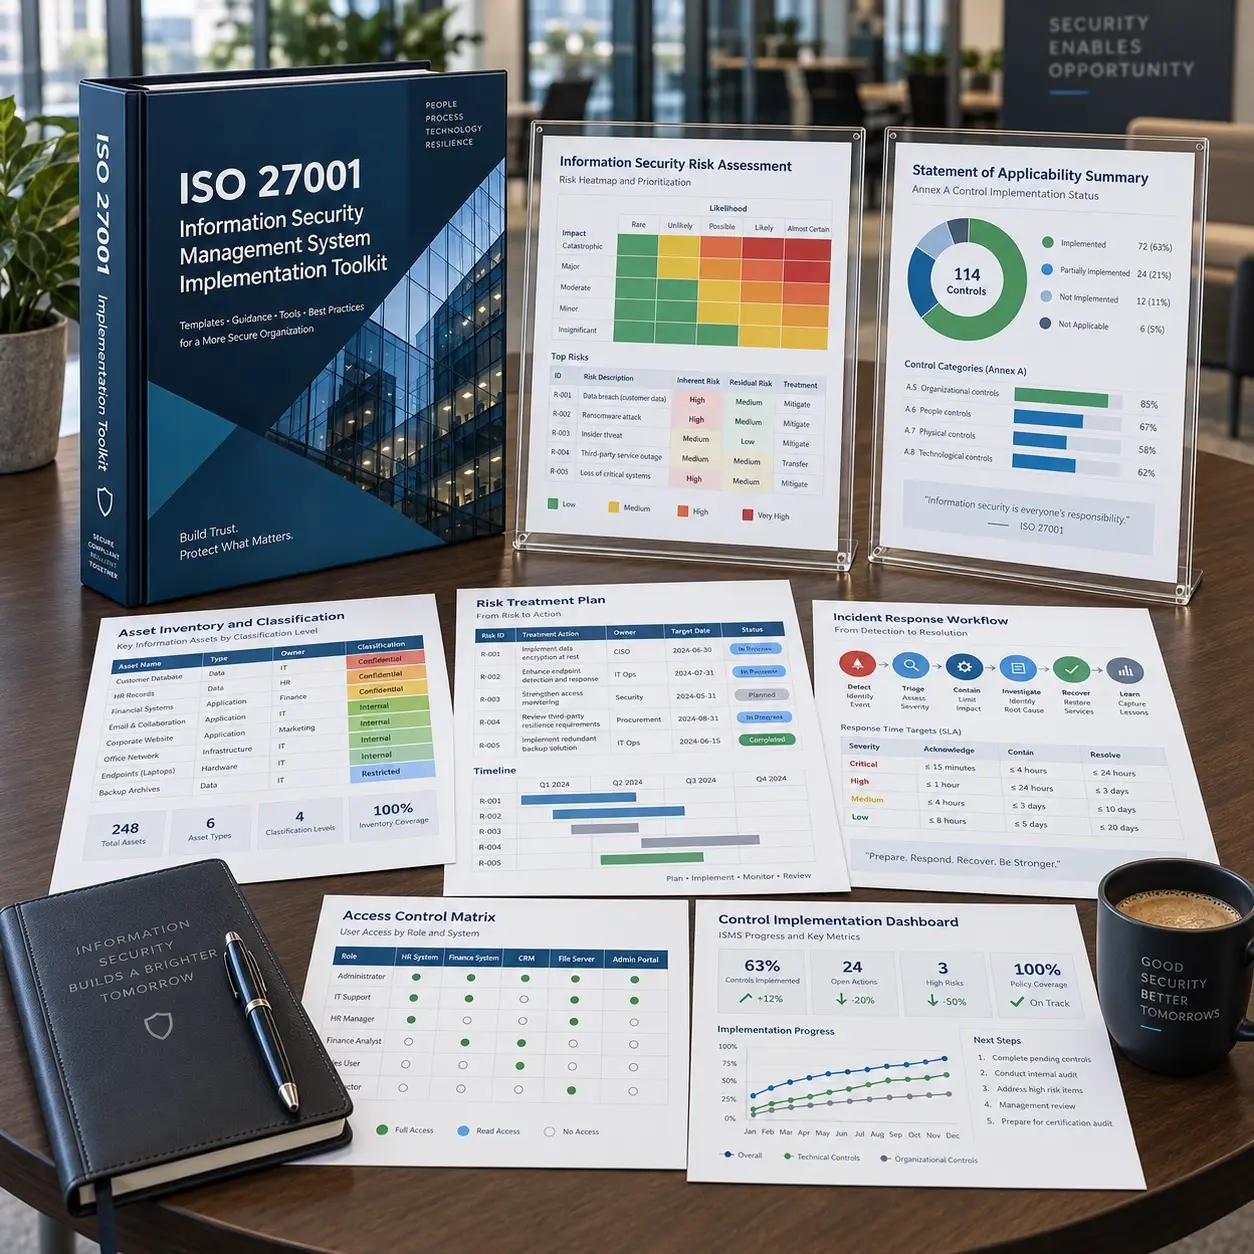
The ISO/IEC 27001:2022 Information Security Management System Toolkit is a comprehensive, Easy To Use documentation package designed to help organizations establish, implement, maintain, audit, and continually improve an effective ISMS.
Aligned with ISO/IEC 27001:2022 requirements, this toolkit supports the full information security management lifecycle, including ISMS scope definition, governance, risk assessment, risk treatment, Statement of Applicability support, Annex A controls, security policies, awareness training, incident management, supplier security, monitoring, internal audit, management review, corrective action, and certification readiness.
Providing complete documentation for the Information Security Management System (ISMS) is often one of the most challenging parts of achieving ISO/IEC 27001 certification, especially for organizations with complex processes, systems, suppliers, assets, regulations, and security control environments.
The ISO/IEC 27001:2022 Information Security Management System Toolkit provides a professionally developed collection of Easy To Use templates and structured implementation documents in editable office formats. It helps your organization accelerate ISMS implementation, standardize risk and control documentation, strengthen audit evidence, improve management reporting, and prepare for ISO/IEC 27001:2022 certification readiness.
Below is the structured list of documents included in the package. Use the quick navigation or expand each part to review the files before downloading the index file.
 Part 1. Implementation Resources
 ISMS Readiness Assessment Questionnaire.docx ISO/IEC 27001:2022 Gap Analysis Checklist.docx Current State ISMS Maturity Assessment Tool.docx Pre-Implementation Site/Department Survey Form.docx Initial Compliance Obligations Mapping Sheet (High-Level).docx Implementation Effort & Timeline Estimation Matrix.docx ISMS Implementation Program Charter.docx ISMS Implementation Steering Committee - Terms of Reference.docx ISMS Implementation Governance Structure & RACI Matrix.docx ISMS Implementation Roles & Responsibilities Register.docx Stakeholder Identification & Analysis Register.docx ISMS Implementation Decision Log.docx ISMS Implementation Work Breakdown Structure (WBS).docx ISMS Implementation Master Schedule & Milestones Plan.docx Detailed Activity & Task Planning Sheet.docx Project Risk & Issue Log (for implementation project).docx Action Item Tracker / To-Do Register.docx Change Request Form (Scope/Cost/Timeline).docx Dependency & Constraint Register.docx Benefits Realization & Success Criteria Register.docx ISMS Implementation Resource Plan (People/Time/Skills).docx ISMS Implementation Competence & Skills Matrix.docx Training Needs Analysis for ISMS Project Team.docx ISMS Implementation Budget Plan & Cost Breakdown.docx External Consultant / Supplier Engagement Plan.docx Time Allocation & Workload Planning Sheet for Key Roles.docx Legal & Regulatory Obligations Alignment Map.docx
 ISMS Implementation Guide and Examples.pdf
 ISO27001 Implementation Guidance.ppt ISO27001 Practical Implementation.pdf
 ISO27001 ISMS gap analysis questionnaire.xlsx ISO27001 implementation project estimator.xlsx ISO27001 Implementation checklist.pdf ISO27001 ISMS implementation and certification process.pdf
Part 2. ISMS Governance and Leadership
ISMS Governance Charter Template.docx ISMS Scope Statement Form.docx Information Security Objectives Register.docx ISMS Governance Operating Model.docx Strategic Alignment Map - Business vs Security Goals.docx Roles and Responsibilities Matrix.docx ISMS Accountability and Ownership Matrix.docx ISMS Committee Terms of Reference (ToR).docx Top Management Commitment Declaration.docx ISMS KPI Dashboard Template.docx ISMS Governance Reporting Calendar.docx Annual ISMS Strategic Plan.docx Resource Allocation Plan for ISMS.docx ISMS Budget Forecasting Template.docx Risk Appetite and Tolerance Statement.docx ISMS Communication Strategy.docx Escalation and Authority Matrix.docx Governance Meeting Agenda.docx Governance Meeting Minutes.docx Policy Management Framework.docx ISMS Maturity Assessment Tool.docx ISMS Review and Improvement Plan.docx Stakeholder Engagement Plan.docx Internal Awareness Letter (CEO/CIO).docx Legal & Regulatory Obligations Alignment Map.docx ISMS_Governance_KPI_Data_Source.xlsx Top_Management_Decision_Tracking_Log.xlsx ISMS_Objectives_Progress_Tracking.xlsx Governance_Meeting_Action_Tracker.xlsx Strategic_Objective_vs_Risk_Alignment_Matrix.xlsx ISMS_Resource_Utilization_Analysis.xlsx Management_Commitment_Evidence_Index.xlsx Governance_Risk_Escalation_Statistics.xlsx
Part 3. Risk Management and Risk Treatment
Risk Management Policy.docx Risk Assessment Methodology.docx Asset Identification and Classification Form.docx Information Asset Register.docx Threat and Vulnerability Assessment Template.docx Risk Register Template.docx Risk Scoring and Prioritization Matrix.docx Risk Treatment Plan (RTP) Template.docx Residual Risk Register.docx Risk Acceptance Form.docx Periodic Risk Review Report.docx Risk Treatment Decision Log.docx Risk Communication Plan.docx Business Risk Exposure Report.docx Risk Owner Assignment Template.docx Risk Monitoring Dashboard.docx Risk Control Gap Analysis.docx Emerging Risk Watchlist.docx Risk Indicator Thresholds Template.docx Risk Treatment Workflow Diagram.docx Risk Evaluation Criteria Template.docx Risk Mitigation Effectiveness Tracker.docx Risk Heatmap Visual Template.docx Control Implementation Tracker.docx Compliance vs Risk Mapping Template.docx Departmental Risk Allocation Matrix.docx Risk Reassessment Schedule.docx Audit Finding to Risk Alignment Register.docx Risk_Scenario_Modeling_Worksheet.xlsx Quantitative_Risk_Impact_Calculation.xlsx Risk_Likelihood_Historical_Data.xlsx Risk_Treatment_Cost_Benefit_Analysis.xlsx Control_Effectiveness_Scoring_Model.xlsx Risk_Trend_Analysis_Dashboard.xlsx Residual_Risk_Change_Tracking.xlsx Risk_Exposure_Forecasting_Model.xlsx
Part 4. Security Policies and Controls
Acceptable Use Policy.docx Access Control Policy.docx Information Classification and Handling Policy.docx Cryptographic Controls Policy.docx Physical and Environmental Security Policy.docx Operations Security Policy.docx Communications Security Policy.docx Mobile Device and Teleworking Policy.docx Bring Your Own Device (BYOD) Policy.docx Secure Development Policy.docx Logging and Monitoring Policy.docx Backup and Restore Policy.docx Asset Management Policy.docx Information Security Policy (Master).docx Secure Disposal and Media Handling Policy.docx Remote Access Policy.docx Patch Management Policy.docx Change Management Policy.docx Third-Party Access Control Policy.docx Cloud Security Policy.docx Incident Management Policy.docx Business Continuity Policy.docx Data Retention Policy.docx Supplier Security Policy.docx Information Transfer Policy.docx Policy Review and Approval Workflow.docx Annex_A_Control_Implementation_Status.xlsx Control_Maturity_Scoring_Model.xlsx Control_Exception_Statistics.xlsx Policy_Compliance_Rating_Sheet.xlsx Control_Ownership_and_KPI_Mapping.xlsx Security_Control_Improvement_Roadmap.xlsx Control_Review_Frequency_Tracker.xlsx
Part 5. Security Awareness and Training
Awareness Program Plan.docx Awareness Training Curriculum Template.docx Training Attendance Register.docx Phishing Simulation Campaign Plan.docx Awareness Effectiveness Survey.docx Knowledge Evaluation Quiz Template.docx Employee Acknowledgment Form.docx Training Completion Certificate Template.docx Targeted Training Plan (for high-risk roles).docx Annual Awareness Report.docx Awareness Communication Calendar.docx Training Material Feedback Form.docx Security Culture Maturity Assessment.docx Departmental Awareness Performance Tracker.docx Awareness FAQ Sheet.docx IT Security Induction Checklist.docx Training_Hours_vs_Role_Analysis.xlsx Awareness_Risk_Role_Mapping.xlsx Phishing_Simulation_Result_Analytics.xlsx Knowledge_Test_Score_Statistics.xlsx Awareness_ROI_Measurement.xlsx Department_Awareness_Maturity_Scoring.xlsx Training_Non-Compliance_Tracking.xlsx
Part 6. Legal, Regulatory and Contractual Compliance
Legal & Regulatory Obligations Register.docx Data Privacy Compliance Matrix (GDPR, PDPA).docx Regulatory Compliance Tracker.docx Intellectual Property Compliance Checklist.docx Data Retention Schedule.docx Contractual Security Clauses Checklist.docx Audit Trail Requirements Register.docx Internal Legal Review Form.docx Data Sharing Agreements Template.docx Privacy Impact Assessment Template.docx Consent Management Log.docx Licensing Compliance Report.docx Regulatory Change Tracker.docx SLA/Contract Review Log.docx IT Compliance Policy.docx External Regulatory Mapping Template.docx Security Exceptions Register.docx Authority Approval Escalation Flow.docx Compliance_Gap_Scoring_Matrix.xlsx Regulation_Applicability_Assessment.xlsx Compliance_Risk_Scoring_Table.xlsx Regulatory_Change_Impact_Analysis.xlsx Contractual_Security_Obligation_Mapping.xlsx Compliance_KPI_Dashboard.xlsx Non-Compliance_Trend_Analysis.xlsx
Part 7. Information Security Incident Management
Incident Management Policy.docx Incident Response Plan (IRP).docx Security Incident Reporting Form.docx Incident Register.docx Incident Classification Criteria.docx Severity Matrix.docx Root Cause Analysis Template.docx Post-Incident Review Form.docx Forensic Readiness Plan.docx Evidence Handling Checklist.docx Incident Communication Plan.docx IRT Roles and Contact List.docx Incident Response Test Plan.docx External Party Notification Log.docx Lessons Learned Log.docx Incident Dashboard.docx Escalation Flowchart.docx Incident Impact Estimation Template.docx Timeline and Containment Report.docx External Legal Reporting Register.docx Incident Simulation Exercise Script.docx Tracking of Repeated Incidents.docx Incident_Trend_Analysis_Dashboard.xlsx Mean_Time_To_Detect_Respond_Report.xlsx Incident_Cost_Impact_Calculation.xlsx Incident_Category_Statistics.xlsx Repeated_Incident_Pattern_Analysis.xlsx Incident_Response_Effectiveness_Score.xlsx Incident_Risk_Linkage_Table.xlsx
Part 8. Business Continuity and Disaster Recovery
Business Continuity Policy.docx Business Impact Analysis (BIA) Template.docx Recovery Time Objective (RTO) Template.docx Recovery Point Objective (RPO) Template.docx Business Continuity Plan (BCP).docx Disaster Recovery Plan (DRP).docx Critical Services Mapping Sheet.docx Emergency Communication Plan.docx Recovery Roles and Contacts List.docx Crisis Management Plan.docx Failover Procedure Checklist.docx System Recovery Checklist.docx Backup and Restore Test Schedule.docx BCP/DRP Training Material.docx Recovery Site Readiness Checklist.docx Downtime Impact Estimation Template.docx DRP Audit Checklist.docx Alternate Site SLA Tracker.docx Annual Continuity Drill Plan.docx Continuity Plan Approval Form.docx Lessons Learned from DR Events.docx BIA_Scoring_and_Prioritization_Model.xlsx RTO_RPO_Achievement_Tracking.xlsx Downtime_Cost_Calculation_Model.xlsx Continuity_Test_Result_Analytics.xlsx DR_Readiness_Maturity_Score.xlsx BCP_Dependencies_Mapping.xlsx Crisis_Response_Performance_Metrics.xlsx
Part 9. Internal Audit and Management Review
ISMS Internal Audit Policy.docx Annual ISMS Audit Plan.docx ISO 27001 Internal Audit Checklist.docx Audit Scope and Objective Definition Template.docx Internal Audit Engagement Letter Template.docx Audit Interview Guide.docx Evidence Collection Log.docx Audit Findings Report Template.docx Non-Conformity Report (NCR) Form.docx Corrective Action Request (CAR) Template.docx Corrective Action Tracker.docx Root Cause Analysis Form for Audit Findings.docx Internal Audit Closure Report.docx Management Review Agenda Template.docx Management Review Minutes Template.docx Performance Metrics Summary Report.docx Compliance Status Summary Template.docx ISMS Status Dashboard.docx Review of Past Action Items Tracker.docx Management Recommendations Log.docx Audit Result Communication Letter.docx Competency Checklist for Internal Auditors.docx Internal Audit Program Maturity Model.docx Audit_Finding_Trend_Analysis.xlsx Audit_Risk_Severity_Scoring.xlsx Corrective_Action_Effectiveness_Measurement.xlsx Audit_Cycle_Time_Analysis.xlsx Department_Audit_Performance_Scorecard.xlsx Management_Review_Decision_Tracking.xlsx ISMS_Performance_Metrics_History.xlsx ISMS Internal Audit Procedure.pdf ISMS Internal Audit Plan.pdf
Part 10. Asset and Configuration Management
Asset Management Policy.docx Information Asset Inventory Sheet.docx Asset Owner Assignment Template.docx Asset Classification and Labeling Guidelines.docx Hardware and Software Register.docx CMDB (Configuration Management Database) Template.docx Software Installation Request Form.docx Software License Register.docx Asset Lifecycle Management Plan.docx Mobile Asset Tracker.docx Removable Media Handling Guidelines.docx Asset Disposal Authorization Form.docx Secure Disposal Certificate Template.docx Asset Transfer Form.docx Lost or Stolen Asset Reporting Form.docx Periodic Asset Revalidation Log.docx Asset Location Mapping Sheet.docx IT Asset Risk Classification Template.docx Configuration Change Log.docx Media Reuse and Sanitization Checklist.docx Unauthorized Asset Detection Log.docx Asset Movement Log Sheet.docx Asset_Risk_Scoring_Model.xlsx Asset_Depreciation_and_Lifecycle_Analytics.xlsx Asset_Control_Coverage_Matrix.xlsx Asset_Change_Frequency_Analysis.xlsx High_Value_Asset_Exposure_Report.xlsx Unauthorized_Asset_Statistics.xlsx Configuration_Drift_Tracking.xlsx
Part 11. Access Control and Identity Management
Access Control Policy.docx User Access Request Form.docx User Access Approval Matrix.docx Identity Lifecycle Management Procedure.docx Access Rights Review Schedule.docx Privileged Access Register.docx Temporary Access Approval Form.docx Access Revocation Form.docx Multi-Factor Authentication (MFA) Deployment Plan.docx Shared Account Usage Policy.docx Joiner-Mover-Leaver (JML) Process Flowchart.docx Privileged Access Management (PAM) Policy.docx Periodic Access Recertification Log.docx Third-Party Access Register.docx Segregation of Duties Matrix.docx Role-Based Access Control (RBAC) Matrix.docx Access Violation Incident Report Form.docx Biometric Access Configuration Sheet.docx Access Log Review Template.docx Identity Governance Audit Checklist.docx Access_Risk_Scoring_Table.xlsx Privileged_Access_Usage_Analytics.xlsx Access_Review_Result_Statistics.xlsx SoD_Violation_Trend_Analysis.xlsx JML_Process_Efficiency_Metrics.xlsx Access_Incident_Correlation_Report.xlsx Identity_Control_Maturity_Score.xlsx
Part 12. Physical and Environmental Security
Physical Security Policy.docx Secure Area Identification Map.docx Access Badge Request Form.docx Physical Access Authorization Matrix.docx Visitor Access Logbook.docx Visitor NDA Agreement Template.docx CCTV Monitoring and Retention Guidelines.docx Data Center Access Procedure.docx Door Access Control Log.docx Server Room Environmental Monitoring Checklist.docx Power Backup System Maintenance Log.docx UPS/Generator Testing Schedule.docx Fire Safety Equipment Checklist.docx Physical Security Incident Register.docx Equipment Relocation Form.docx Theft and Tampering Investigation Form.docx Physical Access Rights Review Template.docx Emergency Evacuation Plan.docx Physical_Access_Risk_Scoring.xlsx Environmental_Monitoring_Data_Log.xlsx Facility_Security_Control_Coverage.xlsx Physical_Incident_Trend_Analysis.xlsx Equipment_Relocation_Risk_Assessment.xlsx Power_and_Environment_Failure_Statistics.xlsx
Part 13. Supplier and Third-Party Security
Supplier Security Policy.docx Supplier Risk Assessment Template.docx Third-Party Security Questionnaire.docx Supplier Pre-Qualification Checklist.docx Information Security SLA Matrix.docx Contractual Security Clauses Template.docx Supplier Compliance Audit Plan.docx Supplier Onboarding Checklist.docx Supplier Exit and Offboarding Form.docx Vendor NDA Template.docx Cloud Vendor Risk Checklist.docx Supplier Access Control Sheet.docx Third-Party Assessment Report Template.docx Service Level Monitoring Report.docx Supplier Segmentation Table (Critical/Non-critical).docx External Data Exchange Register.docx Contract Review and Renewal Tracker.docx Supply Chain Security Risk Register.docx Periodic Supplier Review Form.docx Third-Party Security Breach Notification Form.docx Outsourced Services Inventory Sheet.docx Supplier_Risk_Scoring_Model.xlsx Supplier_Security_Performance_Index.xlsx Third_Party_Control_Coverage_Matrix.xlsx Supplier_Non-Compliance_Trend.xlsx Outsourced_Service_Risk_Exposure.xlsx Supplier_Audit_Result_Analytics.xlsx Supply_Chain_Risk_Heatmap_Data.xlsx
Part 14. Change and Patch Management
Change Management Policy.docx Change Request Form.docx Change Approval Log.docx Emergency Change Authorization Form.docx Change Implementation Plan Template.docx Security Impact Analysis Template.docx Change Review Board (CRB) Meeting Agenda.docx Change Rollback Plan Template.docx Change Implementation Checklist.docx Change Post-Implementation Review Form.docx Unauthorized Change Incident Report.docx Change Conflict Log.docx Change Success Rate Report.docx Patch Management Policy.docx Patch Deployment Schedule.docx Vulnerability to Patch Mapping Sheet.docx Patch Rollback Plan.docx Patch Effectiveness Review Checklist.docx Change_Risk_Scoring_Model.xlsx Failed_Change_Impact_Analysis.xlsx Patch_Compliance_Rate_Statistics.xlsx Vulnerability_Exposure_vs_Patch_Delay.xlsx Emergency_Change_Frequency_Report.xlsx Change_Success_Rate_Dashboard_Data.xlsx
Part 15. Monitoring, Logging, and Review
Logging and Monitoring Policy.docx Event Logging Configuration Guide.docx Security Monitoring Plan.docx SIEM Configuration Documentation.docx Log Review Checklist.docx Anomaly Detection Criteria Template.docx Alert Escalation Flowchart.docx Logging Retention Schedule.docx Centralized Logging Dashboard Template.docx Security Event Summary Report.docx Unauthorized Activity Detection Log.docx Log Source Inventory Sheet.docx Logging Exception Tracker.docx Log Correlation Analysis Template.docx Log Tampering Detection Checklist.docx Alert Response Tracker.docx Daily Security Monitoring Log.docx Monthly Security Trends Report.docx Monitoring System Uptime SLA Report.docx Security_Event_Volume_Trend.xlsx Alert_False_Positive_Analysis.xlsx Log_Source_Coverage_Ratio.xlsx Detection_Time_Analytics.xlsx Monitoring_Control_Effectiveness_Score.xlsx Security_Operations_KPI_Data.xlsx Incident_vs_Log_Correlation_Data.xlsx
Part 16. Documentation and Record Control
ISMS Documentation Control Policy.docx Document Register.docx Version Control Log.docx Document Review and Approval Workflow.docx Document Access Control Matrix.docx Document Archive and Retention Plan.docx Policy Revision Schedule.docx Template Usage Guidelines.docx Controlled Document Distribution Log.docx Obsolete Document Disposal Form.docx SOP Template for Information Security.docx File Naming Convention Standard.docx Departmental Document Index Sheet.docx Backup of Document Repository Log.docx Sensitive Document Access Audit Log.docx Procedure for Electronic Signature Approval.docx Policy and Procedure Change Notification Memo.docx Document_Compliance_Status_Tracking.xlsx Document_Review_Delay_Analysis.xlsx Policy_Update_Frequency_Report.xlsx Document_Access_Statistics.xlsx Controlled_Document_Distribution_Metrics.xlsx Obsolete_Document_Risk_Tracking.xlsx
Part 17. Certification and External Audit Management
ISO 27001 Certification Roadmap.docx Certification Scope Definition Template.docx ISO 27001 Readiness Checklist.docx Stage 1 Audit Preparation Plan.docx Stage 2 Audit Documentation Binder Index.docx External Auditor Engagement Letter Template.docx Certification Audit Schedule.docx Certification Evidence Mapping Sheet.docx Non-Conformity Tracker (External Audit).docx Corrective Action Log (External Audit).docx Auditor Communication Briefing Sheet.docx Pre-Audit Gap Analysis Report.docx Certification Cost Estimation Template.docx Certification Milestone Tracker.docx External Audit Findings Response Template.docx Surveillance Audit Preparation Guide.docx Re-Certification Audit Plan.docx Management Presentation Slide Pack.docx Certification_Readiness_Scoring_Model.xlsx Audit_Evidence_Coverage_Analysis.xlsx External_Audit_Finding_Trend.xlsx Certification_Cost_vs_Benefit_Analysis.xlsx Surveillance_Audit_Preparedness_Index.xlsx Certification_Milestone_Delay_Analysis.xlsxReview the complete file index, preview free sample templates, or check the purchase and payment guide.
| Date File Updated | 25/03/2025 |
| File Format | pdf, xls, doc, docx, xlsx, pptx |
| No. of files | 475 Files, 17 Folders |
| File download size | 20.39 MB (.rar) |
| Language |  English |
| Purchase code | ISO27001-Toolkits |
The ISO Toolkit has helped us structure our implementation work clearly. It gave our team practical templates, organized procedures, and a reliable starting point for building our management system documentation.
After using the ISO Toolkit, our ISO preparation became much more organized. The documents are professional, easy to adapt, and helpful for aligning internal teams around clear compliance requirements.
Our consultants and internal managers found the toolkit very practical. It saved time, improved documentation consistency, and gave us a better framework for ISO implementation across departments.
The toolkit provides a strong foundation for ISO best practices. It helped us organize policies, procedures, records, and improvement actions in a way that is simple to maintain.
The ISO Toolkit brought structure to our compliance documentation and reduced the workload for our implementation team. It allowed us to focus more on improving processes instead of starting documents from scratch.
The ISO Toolkit is practical, well arranged, and easy to customize. It helped replace scattered files with a more complete document set for managing our ISO implementation activities.
The toolkit is very straightforward to use. It gave our team a clear implementation path, helped define responsibilities, and made ISO documentation easier for non-specialists to understand.
The ISO Toolkit gave us a better understanding of management system requirements and provided a user-friendly way to improve processes, controls, and internal documentation.
The toolkit helped me organize our ISO training, document review, and implementation planning. It made the entire preparation process more focused and easier to communicate with the team.
Excellent ISO Toolkit. It is highly useful for managers, consultants, and implementation teams who need practical documents to support ISO certification readiness.
A very useful toolkit and one of the most practical document sets I have used. It provides clear templates that can be adapted quickly for different ISO implementation needs.
These ISO Toolkits increased my confidence in managing implementation work. They helped us prepare documentation, assign responsibilities, and move toward a more mature management system.